- 1Create a free account
- 2Pick your topics and platforms
- 3Read your tailored feed
- 4Ask the CMMCSimple Assistant
Get the feed your contracts depend on
Create a free account, pick your topics, and see your tailored compliance feed today.
Stay ahead of CMMC and DoD cybersecurity developments with AI-powered news aggregation, personalized updates, and source-backed answers.
Deadlines
We polled attendees at our latest CMMC Summit. Their answers show where the DIB stands nearly four months after the July 13 Phase 2 pause. Some highli...We polled attendees at our latest CMMC Summit. Their answers show where the DIB stands nearly four months after the July 13 Phase 2 pause. Some highlights: 87% kept their #CMMC work moving after the pause. 66% have budgeted under $50,000, up from 62% in...
PreVeil (LinkedIn) · Nov 11, 2026

Rulemaking
Why DoD paused CMMC: inside the RFI results with Jason MillerWe'll say it again: the CMMC Phase 2 pause affects the C3PAO assessment requirement but does not change your DFARS 7012 obligations. NIST SP 800-171, SPRS scoring, and FedRAMP Moderate equivalency still apply, and the False Claims Act is still holding contractors accountable. Jason Miller, Executive Editor at Federal News Network, joins That CMMC Show to walk through his two-part FNN series on the pause. His reporting draws on DoD’s own RFI summaries and task force recommendations. We cover: • Why the pause happened, according to Jason’s sources • What the RFI found on cost: about $47,000 on average for a Level 2 assessment, versus SBA’s estimate of up to $600,000 • Whether there are enough assessors (the RFI says yes) • Options on the table, including a phased Level 2 restart for a subset of contractors and grant or loan programs for small businesses • How Rev 2 vs. Rev 3 and the coming FAR CUI rule could split requirements across DoD and civilian work 0:00 Intro: Jason Miller, Federal News Network 2:39 What the pause changed and what it didn’t 3:35 Why DoD paused CMMC 8:53 The cost question: $600K vs. $47K 10:03 Contractors pulling back on DFARS 7012 work 11:30 Why DoD h
Summit 7 (YouTube) · Nov 11, 2026
GovCon & Trade · Nov 5, 2026

Summit 7 (YouTube) · Nov 5, 2026

Summit 7 (YouTube) · Nov 5, 2026

Google Workspace Updates / Product Announcements · Nov 5, 2026
Chat in plain English and get answers grounded in the latest coverage, with source links. No account needed to try it. News awareness only, not legal or compliance advice.
Cyber News
Dark Reading · Nov 12, 2026

Cyber News
As AI model training and distillation increase, AI tokens are becoming a piping hot currency for threat actors. Cloud hosting provider Railway found out the hard way; it has confirmed a near 26-hour battle against attackers targeting AI provider credentials to sell to AI ‘transfer stations’ for use in model distillation. The crooks generated about $740,000 in fraudulent AI usage charges using the stolen credentials and potentially had access to up to 100,000 workspace credentials. Railway said the attacker’s database searches looked for AI provider keys by name before anything else; some queries also targeted cloud, database, and payment service credentials. The company disclosed the incident on October 22 , and posted a follow-up report this week. Because of the ongoing investigation, it is not able to share the specific details and scale of the exploits, but advised users to revoke and reapply sensitive environmental variables stored on Railway prior to October 21. “AI credentials are becoming the new credit card numbers,” said David Shipley of Beauceron Security. “So-called LLMjacking is expected to displace Cryptojacking as a cheap, scalable way to make money.” A 26-hour battle
CSO Online · Nov 12, 2026
Threat Intelligence
SANS Internet Storm Center · Nov 12, 2026
Government Cloud
Align event registrations with the way your organization manages customer data. By supporting lead-based registration journeys and existing matching rules, you can avoid unnecessary Contact creation, improve data quality, and ensure event attendees follow the same lead management process used across your business. Configure event registration forms to create or update Contacts, Leads, or both Leads and Contacts Apply existing matching, deduplication, and update rules to event registrations for more consistent and accurate customer data. Register attendees without requiring a Contact record, enabling lead-only registration scenarios and sales-driven qualification processes. GA date: June CY2027 Preview date: February CY2027
Microsoft 365 for US Government Service Descriptions · Nov 12, 2026
Government Cloud
Organizations managing high volumes of project transactions need to retain historical cost data without allowing years of completed transactions to continually increase the volume of active operational data. This capability enables organizations to archive processed project staging table cost actuals for long-term retention while preserving access to historical records when needed. Administrators can archive eligible project cost actuals for selected legal entities and date ranges using the Archive with Dataverse long-term retention workspace. The archive process moves eligible cost actuals and related transaction records to long-term storage, while providing visibility into job status and progress and continued access to archived records after the process completes. This capability helps organizations manage growing project transaction volumes while retaining the historical cost information required for financial history, audit, and business needs. It is available for Dynamics 365 Project Operations deployments that work with other Dynamics 365 ERP applications and requires Archive with Dataverse long-term retention. GA date: March CY2027 Preview date: September CY2026
Microsoft 365 for US Government Service Descriptions · Nov 12, 2026
Government Cloud
Copilot Chat in Outlook on iOS and Android is getting updated! You'll notice smoother animations, improved strings, and some small changes to the header, such as the new/temporary chat button being moved behind the ... button. GA date: December CY2026
Microsoft 365 for US Government Service Descriptions · Nov 12, 2026
Government Cloud
Deduplicates recipients by contact point, so each phone number or custom channel address gets the message once per send. Eliminates manual post-send clean-up, wasted messaging spend and the customer annoyance of duplicate texts. Brings SMS and custom channels to parity with email's built-in deduplication. GA date: December CY2026
Microsoft 365 for US Government Service Descriptions · Nov 12, 2026
Government Cloud
Segment templates help you build audiences without recreating queries for each campaign. Choose a built-in template for common scenarios such as event attendance or email engagement, or save your own segment query as a reusable custom template. Add placeholders with hint text to guide marketers through entering campaign-specific values, reducing repetitive setup while keeping audience criteria consistent. GA date: November CY2026
Microsoft 365 for US Government Service Descriptions · Nov 12, 2026
Government Cloud
In learning activities, students can rehearse presentations, receive feedback on their delivery, and practice again with targeted suggestions to improve clarity and confidence. #education GA date: December CY2026
Microsoft 365 for US Government Service Descriptions · Nov 12, 2026
Government Cloud
Adding easy access to top sites in Edge search bar on desktop. Users can add, edit, remove, or hide top sites. Admins can control available to this feature using the NewTabPageManagedQuickLinks and NewTabPageQuickLinksEnabled policies. GA date: January CY2027
Microsoft 365 for US Government Service Descriptions · Nov 12, 2026
Government Cloud
Power Automate will support Delinea Secret Server as an external credential provider for desktop flows. Organizations can securely use credentials managed in Delinea for machine sign-in and credential retrieval during attended and unattended automation. GA date: March CY2027
Microsoft 365 for US Government Service Descriptions · Nov 12, 2026
Government Cloud
Desktop flows will support direct triggers, enabling automations to start in response to supported events without requiring an intermediary cloud flow. This simplifies automation design and reduces the effort required to connect desktop flows to business processes. GA date: March CY2027 Preview date: January CY2027
Microsoft 365 for US Government Service Descriptions · Nov 12, 2026
Government Cloud
The write to business rules engine configuration experience introduces an option to submit only records that have successfully passed Account structure validation. When enabled, Business Performance Planning filters the writeback dataset and submits only records marked as valid by account structure validation to the business rules engine writeback process. Records that have not passed validation are excluded from the submission so users can review and correct them before attempting to write them to Dynamics 365 Finance. More info: https://learn.microsoft.com/en-us/dynamics365/finance/business-performance-planning/bpp-bud-reg-write GA date: November CY2026
Microsoft 365 for US Government Service Descriptions · Nov 12, 2026
Government Cloud
Bring Minecraft Education to every classroom with AI-powered tools that match curriculum goals to Build Challenges, blend lessons with project-based learning, launch directly from Learning Zone, and give you full visibility into participation, completion, and student understanding. #education GA date: February CY2027
Microsoft 365 for US Government Service Descriptions · Nov 12, 2026
Government Cloud
Cross-Tenant Orchestrated Migration for User Data Migration (UDM) and Shared Data Migration (SDM) allows customers to move their Microsoft 365 data from one Microsoft tenant to another. UDM includes the ability to move user mailboxes, OneDrive accounts, Teams chats, and Teams meetings. SDM includes the ability to move M365 Groups, SharePoint Sites, Group Mailboxes, and teams and channels. More info: TBD GA date: December CY2026
Microsoft 365 for US Government Service Descriptions · Nov 12, 2026
Cyber News
The CCP built a Big Data system to scrape reams of information and learn about individuals abroad, to potentially target and exploit them. Think Alice Huang Lite.
Dark Reading · Nov 12, 2026
Cyber News
The package adds public-private cyber responders, an AI-focused team run by the economic ministry, and more leeway to use the government's new active cyber-defense powers.
Dark Reading · Nov 11, 2026
Government Cloud / Cloud Security
DeepReinforce AI's Ornith-1.0-9B and Ornith-1.0-35B models are now available on Amazon SageMaker JumpStart, expanding the portfolio of foundation models available to AWS customers. These two models are part of the Ornith 1.0 family of open-source, self-scaffolding agentic coding models released under the MIT license, achieving state-of-the-art performance among open-source models of comparable size on coding benchmarks such as Terminal-Bench 2.1, SWE-Bench, NL2Repo, and OpenClaw. These models address different agentic coding challenges with specialized capabilities: Ornith-1.0-9B is a lightweight 9B-parameter dense model post-trained on Qwen 3.5 9B, designed for efficient single-GPU deployment. With a 256K-token context window and 32 decoder layers, it is well-suited for individual developers and small teams running agentic coding workflows on a single GPU — including laptops with consumer-grade hardware. Its self-improving training framework uses reinforcement learning to jointly optimize scaffold generation and solution rollouts, enabling the model to discover better search trajectories and generate higher-quality code solutions. Ornith-1.0-35B is a 35B-parameter Mixture-of-Exper
AWS What's New (Recent Announcements) · Nov 11, 2026
Government Cloud / Cloud Security
DeepSeek's DeepSeek-V4-Pro, DeepSeek-V4-Flash, and DeepSeek-V4.1-Flash models are now available on Amazon SageMaker JumpStart, expanding the portfolio of foundation models available to AWS customers. These three open-weight Mixture-of-Experts (MoE) language models, released under the MIT license, deliver frontier-class performance across reasoning, coding, and agentic workloads while activating only a fraction of their total parameters per token, enabling high efficiency at scale. These models address different AI challenges with specialized capabilities: DeepSeek-V4-Pro is designed for complex reasoning and high-quality text generation at flagship scale. This 1.6T-parameter MoE model activates 49B parameters per token and supports a 1M-token context window, making it well-suited for long-document analysis, multi-step reasoning, and demanding generation tasks that require maximum model capacity. DeepSeek-V4-Flash delivers strong performance at significantly lower compute cost as an efficient 284B-parameter MoE model activating 13B parameters per token. It supports the same 1M-token context window as V4-Pro, making it ideal for latency-sensitive and cost-conscious production deploym
AWS What's New (Recent Announcements) · Nov 11, 2026
Cyber News
The Baker Tilly Advisory Group is notifying clients that a data breach has compromised certain personal information about them and their dependents.
BleepingComputer · Nov 11, 2026
Threat Intelligence
Learn what Unit 42 discovered about attacker use of AI-powered red team tools, and how to mitigate these attacks.
Palo Alto Unit 42 · Nov 11, 2026
Cyber News
ConnectWise is investigating an active malware campaign targeting managed service providers (MSPs) that uses compromised ScreenConnect environments to deploy rogue remote-access clients to customer devices.
BleepingComputer · Nov 11, 2026

Government Cloud
Earlier this year we introduced Sheets canvas , which uses Gemini to turn spreadsheet data into interactive mini-apps like dashboards, kanban boards, and calendars. Starting today, you can publish a Sheets canvas directly to its own link, granting others read-only access to interact with the mini-app without sharing the full source spreadsheet. The published link is separate from the spreadsheet URL and has its own audience setting, so you can publish a canvas to your whole organization even if the file itself is shared with a smaller group. For example: An events coordinator can publish a conference agenda as a filterable schedule for hundreds of attendees while only the planning team edits the source sheet. A program manager can publish a launch timeline from the team's tracker, giving stakeholders across the company a live view of milestones without edit access to the spreadsheet. A learning and development lead can publish a course calendar so anyone in the company can see upcoming sessions, while the training team manages the data source. You can only publish a Sheets canvas that you have edit access to. To publish, click the icon in the canvas toolbar, then click the “Publish
Google Workspace Updates / Product Announcements · Nov 11, 2026
Government Contracting
Welcome to The Covington Monthly Protest 3-Pack, which highlights (in 500 words or less) three significant bid protest decisions released in the prior month and offers key takeaways. The October 2026 picks illustrate: (1) How an ill-designed attempt to fix an inadvertent spill of contractor proprietary information can doom a procurement award; (2) The dangers...
Inside Government Contracts · Nov 11, 2026
Cyber News
Certificate authority eMudhra has revoked eight additional intermediate CA certificates after an investigation into its recent certificate security incident found improper handling of private keys during the certificate-generation process.
BleepingComputer · Nov 11, 2026
Cyber News
An organization's ability to quickly recover from a business disruption will be a competitive advantage in an era of AI-driven threats and business enablement.
Dark Reading · Nov 11, 2026
Government Cloud
You can now use numbered lists and nested lists in your Google Chat messages. Numbered lists work well for step-by-step instructions, rankings, and agendas. Nested lists let you break a main point into smaller details, which helps for meeting notes, project plans, and status updates. You can mix bulleted and numbered lists in the same message and nest items up to five levels deep. Start a numbered list from the formatting toolbar or by typing "1." at the start of a line. Lists can be created in Google Chat on the web and will display for everyone in the conversation on web, Android, and iOS. Support for creating lists on Android and iOS will follow. Getting started Admins: There is no admin control for this feature. End users: There is no end user setting for this feature. Visit the Help Center to learn more about formatting messages in Google Chat . Developers: Chat apps can send numbered and nested lists using standard Markdown syntax through the Google Chat API. Visit the Google Chat API documentation to learn more . Rollout pace Rapid Release and Scheduled Release domains: Gradual rollout (up to 15 days for feature visibility) starting on November 10, 2026 Availability Availabl
Google Workspace Updates / Product Announcements · Nov 11, 2026
Cloud Security
Bulletin ID: 2026-180-AWS Publication Date: 11/11/2026 13:00 PM PST Description: MServer-side request forgery (SSRF) in the server registration and update API in Amazon mcp-gateway-registry before 1.35.0 might allow an authenticated remote user to send requests from the gateway to internal network services and cloud instance metadata endpoints and read the responses via a crafted request Impacted versions: >= v1.0.3 AND <= 1.34.0 Refer to the article for the most up-to-date and complete information.
AWS Security Bulletins · Nov 11, 2026
Cloud Security
Bulletin ID: 2026-179-AWS Publication Date: 11/11/2026 12:30 PM PST Description: Missing authorization in the external management API in Amazon mcp-gateway-registry 1.0.9 through 1.24.7 might allow an authenticated remote user to assign the registry administrator scope to their own identity group and obtain administrative control of every registered gateway asset via a crafted group import request. Impacted versions: >= 1.0.9 AND <= 1.24.7 Refer to the article for the most up-to-date and complete information.
AWS Security Bulletins · Nov 11, 2026
CMMC
We polled attendees at our latest CMMC Summit. Their answers show where the DIB stands nearly four months after the July 13 Phase 2 pause. Some highlights: 87% kept their #CMMC work moving after the pause. 66% have budgeted under $50,000, up from 62% in 2025 and 49% in 2024. 49% already use AI to draft their security plans and policies. Read the full report → https://lnkd.in/ec6JzQPS
PreVeil (LinkedIn) · Nov 11, 2026
Government Cloud / Cloud Security
AWS Network Security Manager is now available in AWS European Sovereign Cloud Region and Thirty-One new Regions Today, AWS announces the general availability of AWS Network Security Manager in the AWS European Sovereign Cloud Region and additional regions. Network Security Manager is a comprehensive network security management solution designed to simplify security policy deployment and enforcement at scale. Network Security Manager supports AWS WAF and AWS Shield in AWS European Sovereign Cloud Region. The additional regions are: US East (Ohio); US West (N. California); US West (Oregon); Asia Pacific (Mumbai); Asia Pacific (Hong Kong); Asia Pacific (Taipei); Asia Pacific (Seoul); Asia Pacific (Osaka); Asia Pacific (Hyderabad); Asia Pacific (Singapore); Asia Pacific (Sydney); Asia Pacific (Melbourne); Asia Pacific (Malaysia); Asia Pacific (New Zealand); Asia Pacific (Thailand); Asia Pacific (Johor); Asia Pacific (Tokyo); Canada (Central); Canada West (Calgary); Mexico (Central); Europe (Frankfurt); Europe (Zurich); Europe (Stockholm); Europe (Ireland); Europe (Milan); Europe (Spain); Europe (London); Europe (Paris); Israel (Tel Aviv); South America (São Paulo), Africa (Cape Town)
AWS What's New (Recent Announcements) · Nov 11, 2026
Cyber News
Notion, the digital workspace platform, disclosed that a security breach at its AI infrastructure provider, Fireworks AI, exposed Notion AI chat transcripts in a small number of workspaces.
BleepingComputer · Nov 11, 2026
Defense News
One industry source told Breaking Defense that the reason for the spate of new loan announcements is that the Pentagon “needed to finalize loans by the end of the fiscal year.”
Breaking Defense · Nov 11, 2026
Cyber News
The RMM provider also released a hotfix as one of recommended mitigations to address public exploits for the alleged zero-days that allow for attacker takeover.
Dark Reading · Nov 11, 2026
Government Cloud / Cloud Security
AWS Cloud WAN now supports VPC Flow Logs, giving you central visibility into IP traffic across your global network. Flow Logs capture detailed information for each flow, so you can understand how traffic moves across your core network without leaving your AWS Cloud WAN account. Until now, network administrators had to stitch together VPC Flow Logs from many VPCs, accounts, and Regions to see traffic across their global network. They often depended on other teams for access to those logs. Cloud WAN Flow Logs give core network owners one consolidated view of traffic between VPCs, Regions, and on-premises networks connected over AWS Direct Connect, AWS Site-to-Site VPN, or SD-WAN. You can use this data to troubleshoot connectivity and performance problems, plan capacity from historical bandwidth trends, find unusual traffic patterns, and keep records for security and compliance. Flow log records include IP addresses, ports, protocol, traffic volume, and packet-loss counters, along with Cloud WAN metadata such as segment, Region, service insertion hops and attachment details. You can turn on Flow Logs for an entire core network, a single core network edge, or individual attachments. Yo
AWS What's New (Recent Announcements) · Nov 11, 2026
Cloud Security
Starting on Amazon Web Services (AWS) is now more straightforward and more secure by default than it’s ever been. Over the past several months, we rolled out a new AWS experience that changes how you start building. It brings together a set of sensible, secure defaults, and taken one at a time, it’s easy to
AWS Security Blog · Nov 11, 2026

Threat Intelligence
Threat actors are deploying GSocket on compromised Linux servers to keep encrypted remote access after the original vulnerability is patched. Learn how to detect, investigate, and remediate this activity.
Microsoft Security Blog · Nov 11, 2026
Government Cloud / Cloud Security
Amazon Elastic Kubernetes Service (Amazon EKS) now offers a larger 24 GB etcd database, up from 16 GB, for 4XL and 8XL Provisioned Control Plane clusters. etcd is the key-value store in the Kubernetes control plane that holds your cluster state, so its size limits how many Kubernetes objects your cluster can store. With 50% more capacity, you can run bigger clusters with more pods, jobs, events, and custom resources. The larger database gives more headroom to workloads that create and update many Kubernetes objects, such as large-scale AI/ML training and inference, batch processing, and CI/CD pipelines. When the etcd database fills up, you can’t add or change objects in your cluster, so the extra headroom helps keep these workloads running as they scale. To get the larger database, choose the 4XL or 8XL tier of Provisioned Control Plane on a cluster running EKS version 1.34 or later. Existing clusters on the 4XL and 8XL tiers running these versions get the larger database automatically, with no action required. The 24 GB etcd database is available in all commercial AWS Regions where Provisioned Control Plane is available. To learn more, see the Amazon EKS Provisioned Control Plane
AWS What's New (Recent Announcements) · Nov 11, 2026
CMMC
We'll say it again: the CMMC Phase 2 pause affects the C3PAO assessment requirement but does not change your DFARS 7012 obligations. NIST SP 800-171, SPRS scoring, and FedRAMP Moderate equivalency still apply, and the False Claims Act is still holding contractors accountable. Jason Miller, Executive Editor at Federal News Network, joins That CMMC Show to walk through his two-part FNN series on the pause. His reporting draws on DoD’s own RFI summaries and task force recommendations. We cover: • Why the pause happened, according to Jason’s sources • What the RFI found on cost: about $47,000 on average for a Level 2 assessment, versus SBA’s estimate of up to $600,000 • Whether there are enough assessors (the RFI says yes) • Options on the table, including a phased Level 2 restart for a subset of contractors and grant or loan programs for small businesses • How Rev 2 vs. Rev 3 and the coming FAR CUI rule could split requirements across DoD and civilian work 0:00 Intro: Jason Miller, Federal News Network 2:39 What the pause changed and what it didn’t 3:35 Why DoD paused CMMC 8:53 The cost question: $600K vs. $47K 10:03 Contractors pulling back on DFARS 7012 work 11:30 Why DoD h
Summit 7 (YouTube) · Nov 11, 2026
Defense News
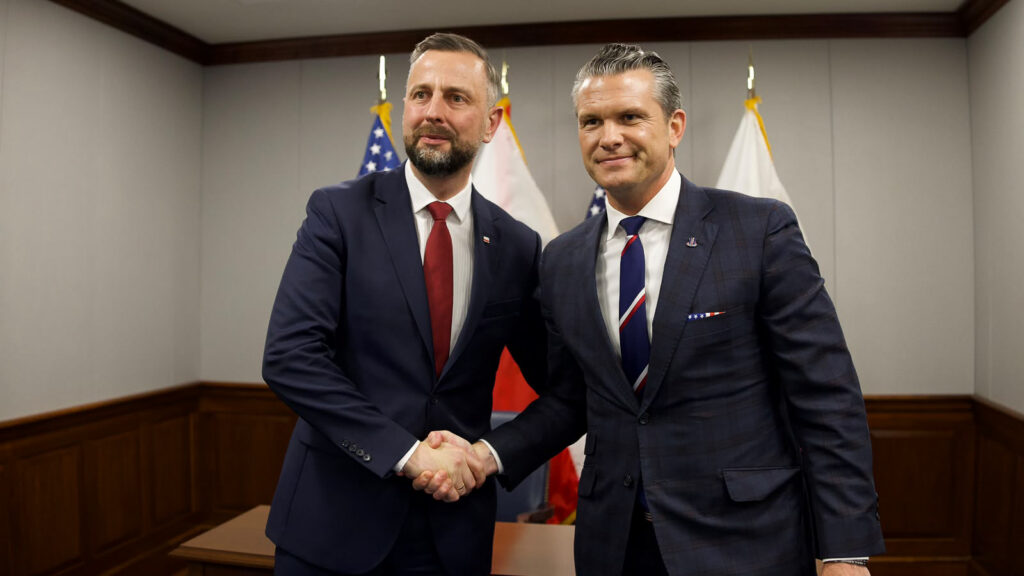
Warsaw has identified four potential locations for a base that could accommodate 5,000 US troops and their families, and is offering to spend up to $4.4 billion on supporting infrastructure.
Breaking Defense · Nov 11, 2026
Government Cloud / Cloud Security
Amazon Cognito now supports session management for user pools, giving you visibility into and control over the sessions your users establish when they sign in to your applications. Single sign-on (SSO) sessions are created when a user signs in through managed login and let them access other app clients without re-authenticating. Token sessions are created when a user signs in to an app client and receives tokens. Session management lets you list a user's active SSO and token sessions across all devices and app clients and revoke any of them on demand. You can also now configure how long each app client reuses an SSO session before requiring re-authentication, instead of the previous fixed one-hour duration. Each session includes details such as session type, app client ID, device type, last activity time and location, and initial sign-in time, so you can build your own end-user or admin session experiences. You can revoke an individual session, optionally with its linked sessions, or use global sign-out to end all sessions associated with one user. You can also set a maximum number of active token sessions per user. Session management is available for user pools in the Essentials o
AWS What's New (Recent Announcements) · Nov 11, 2026
Defense News
The new fiscal uplift comes in the wake of Ukraine President Volodymyr Zelenskyy telling European leaders last month that “we need at least €70 billion more from you.”
Breaking Defense · Nov 11, 2026
Cloud Security
Over the past few weeks, I’ve introduced you to people who fell into security from the most unexpected places, who work in domains you’ve probably never heard of, and who were honest about what the job is like after the excitement fades and the real work begins. This is the final post in a four-part
AWS Security Blog · Nov 11, 2026
Cyber News
The cybercrime group Qilin has emerged as the world's most active ransomware affiliate program, claiming at least 365 victim organizations in the past three months alone. But even top Russian hackers make operational security mistakes, and the administrator of Qilin has made a few key missteps over the last decade that all point to a 36-year-old man living in St. Petersburg, Russia.
Krebs on Security · Nov 11, 2026
Defense News
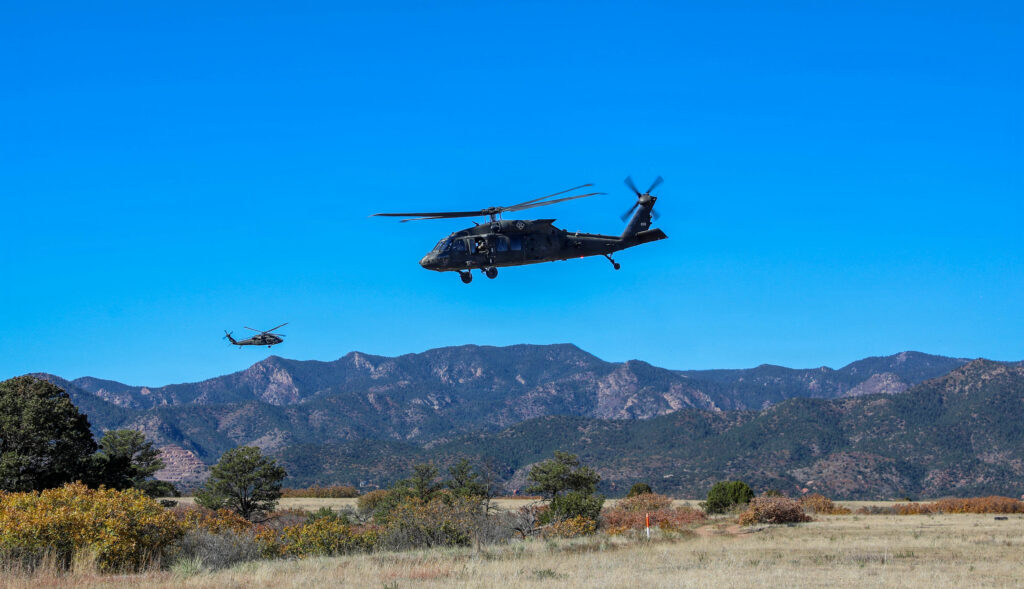
Breaking down stovepipes, managing data and enabling better decision making are key components of the Army’s NGC2 plan.
Breaking Defense · Nov 11, 2026
Government Cloud / Cloud Security
AWS Lambda MicroVMs now supports the x86 CPU architecture, so you can run your existing x86 applications, tools, and software dependencies without recompiling or porting them. When you create a MicroVM image, you can now choose between x86 and Arm (AWS Graviton) to give each user or job an isolated MicroVM on the architecture your workload uses. Lambda MicroVMs is a serverless compute primitive that provides VM-level isolation, near-instant launch and resume, and state preservation for running user or AI-generated code, in applications such as AI coding assistants, CI/CD runners, interactive development environments, and vulnerability scanners. Today’s launch enables you to run x86-based workloads on Lambda MicroVMs as-is. For workloads that run on Arm, you can continue using AWS Graviton processors which is the default CPU architecture option. To start building x86 workloads on Lambda MicroVMs, choose the x86 architecture when you create a MicroVM image from your Dockerfile, then launch MicroVMs from that image. You can use MicroVMs through the AWS Lambda console, AWS CloudFormation, AWS Cloud Development Kit, or with your preferred agentic development tools using the Agent Toolki
AWS What's New (Recent Announcements) · Nov 11, 2026
Defense News
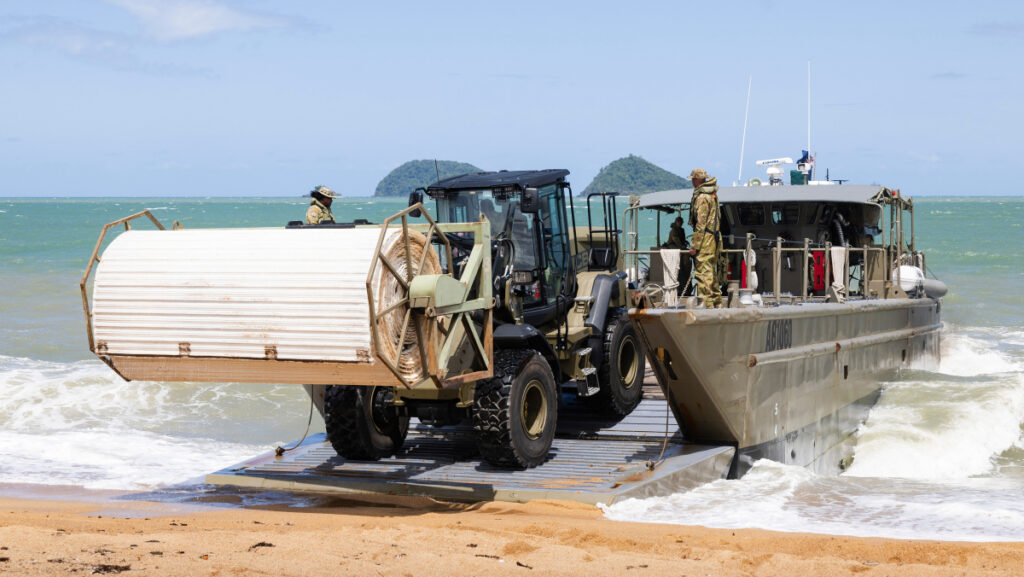
The introduction of two new classes of landing craft would introduce capabilities that the Australian Army has not operated in recent times, an expert told Breaking Defense.
Breaking Defense · Nov 11, 2026
Government Cloud / Cloud Security
Amazon EKS Auto Mode now supports security groups for Pods, letting you apply dedicated Amazon EC2 security group rules to individual Pods. Different workloads on the same node can carry different security groups, giving your Pods network-level segmentation without creating separate node pools for each application. Security groups for Pods extends your existing AWS network controls to the Pod level, so your Pods can reach resources such as Amazon RDS and Amazon ElastiCache databases that authorize connections by security group under the same rules the rest of your VPC uses. You define which Pods receive which security groups with a SecurityGroupPolicy resource, and Pods not matched by a policy keep using their node’s security groups. Security groups for Pods is included as part of EKS Auto Mode at no additional charge and is available on clusters running Kubernetes version 1.36 or later, in all AWS Regions where EKS Auto Mode is supported. To learn more, see Security groups for Pods in the Amazon EKS User Guide and the Amazon EKS Auto Mode product page.
AWS What's New (Recent Announcements) · Nov 11, 2026
Defense News
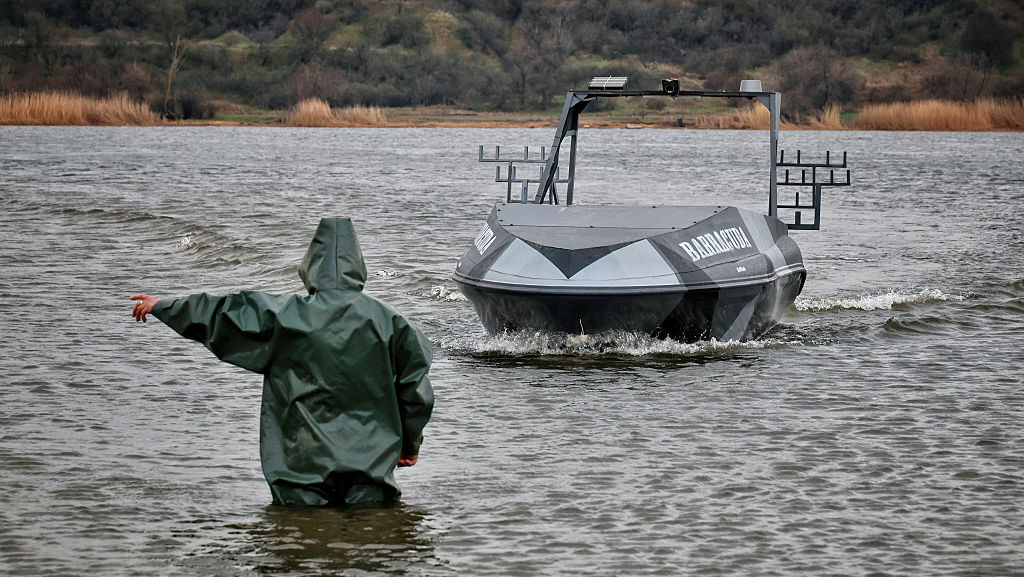
“What we’ve done so far, we took some experience from Ukraine, for example, where we hid some Ukrainian forces and Ukrainian-made USVs, and made them the red team against the blue force of NATO,” Adm. Pierre Vander told Breaking Defense.
Breaking Defense · Nov 11, 2026
Create a free account, pick your topics, and see your tailored compliance feed today.
Want to publish your news with CMMCSimple? Contact us at news@cmmcsimple.com.
Our RSS source list is reviewed and updated every two weeks on Friday, so newly accepted feeds appear with the next update.
© 2026 CMMCSimple