- 1Create a free account
- 2Pick your topics and platforms
- 3Read your tailored feed
- 4Ask the CMMCSimple Assistant
Get the feed your contracts depend on
Create a free account, pick your topics, and see your tailored compliance feed today.
Stay ahead of CMMC and DoD cybersecurity developments with AI-powered news aggregation, personalized updates, and source-backed answers.
Ecosystem
Launch Of Nationwide Assessment To Dismantle Barriers To Additive Manufacturing In Defense ProductionThe War Department, in partnership with the Commerce Department's Bureau of Industry and Security, announced a national assessment to identify and dismantle the qualification cost and timeline barriers hindering the scaling of additive manufacturing across...
DoD News Releases · Nov 16, 2026
Ecosystem
CMMC Accreditation Body Endorses Pentagon’s Proposed Implementation Changes in CMMC 2.0 - November 04, 2021Ecosystem
CMMC Accreditation Body Appoints Melanie Kyle Gingrich as First Vice President for Training and... - May 13, 2021Rulemaking
CMMC “Delta” Assessments: What the Final Rule Says About Changes
Summit 7 (YouTube) · Nov 11, 2026
PreVeil (LinkedIn) · Nov 11, 2026

Summit 7 (YouTube) · Nov 11, 2026
The Cyber AB — Training, Certification & Press
Breaking Defense · Nov 10, 2026

PreVeil Blog · Nov 10, 2026
Chat in plain English and get answers grounded in the latest coverage, with source links. No account needed to try it. News awareness only, not legal or compliance advice.
Cyber News
In breach notification letters, the rideshare company said it was notified by a third party service provider on October 9 that internal credentials were stolen and used to access Uber’s account.
The Record · Nov 18, 2026
Cyber News
Anthropic will publicly disclose high- and critical-severity vulnerabilities it reports to vendors and open source maintainers after 30 days, down from 90. Every other bug it reports gets 45 days. The new deadlines cover reports sent on or after January 1, 2027, and reports already open on that date keep the deadlines they started with. The company says it no longer expects a reported vulnerability to stay private for months, because a bug one model
Help Net Security · Nov 17, 2026

Cyber News
ConnectWise on Monday said it completed its investigation into unauthorized access targeting partner ScreenConnect environments, and recommended customers to ensure that the technician client is running version 26.6.5 or later. The company said additional activity targeting on-premises environments continues to be reported where the identified third-party extensions remain enabled, and
The Hacker News · Nov 17, 2026

Cyber News
Seed deals for cybersecurity startups dipped slightly in the third quarter of 2026, the second decline in a row, while the wider U.S. venture market had one of its best quarters since 2021. Investment firm DataTribe tracked the split using PitchBook data on U.S. seed through Series E rounds, and sorted the cyber seed deals into categories. Across the market, capital is pooling in fewer, larger rounds, and the bar for the round after seed
Help Net Security · Nov 17, 2026
Cyber News
Microsoft has expanded Windows Autopatch’s quality update controls, allowing administrators to manage Windows quality updates, supported .NET Framework updates, and Quick machine recovery updates through a single policy in Microsoft Intune. Windows Autopatch is a cloud service that automates updates for Windows, Microsoft 365 Apps for enterprise, Microsoft Edge, and Microsoft Teams to help improve organizational security and productivity. The new controls support automatic or manual approval for different update types, alongside device monitoring through
Help Net Security · Nov 17, 2026

Cyber News
99% of organizations use AI agents to perform autonomous or semiautonomous actions in development pipelines, according to Palo Alto Networks’ State of Cloud Security Report 2026. Meanwhile, 82% say AI-driven development has increased the volume of updates to cloud infrastructure. Release pressure leaves security issues unresolved AI’s role in cloud development now extends to designing architectures and automatically deploying applications to production. Nearly three-quarters of organizations grant agents permission to modify code, CI/CD configuration or
Help Net Security · Nov 17, 2026

Cyber News
N-able has released a new security update to address additional critical security flaws impacting N-central. Describing N-central 2026.4 Hotfix 3 as a critical security update, the company said it includes a number of security patches and fixes that enhance the security of the Remote Monitoring and Management (RMM) and Unified Endpoint Management (UEM) platform. "HF3 builds on the
The Hacker News · Nov 17, 2026
Cyber News
Cybersecurity Architect Peraton | USA | On-site – View job details As a Cybersecurity Architect, you will integrate security into DevSecOps, implement and maintain security controls, and manage ATO packages in accordance with DoD, DAF and customer requirements. You will develop security plans and procedures, assess risks, and apply expertise in systems, networks and incident response to address complex cybersecurity challenges. Cyber Security Engineer Rozmith | USA | Remote – View job details As a
Help Net Security · Nov 17, 2026

Cyber News
A suspected supply chain attack targeting Optimizely has led to malicious JavaScript being loaded on numerous popular websites, including Zoom, CNN, Fox News, BBC, Salesforce, and GitLab, exposing visitors to scripts designed to steal cryptocurrency and payment information and exploit vulnerabilities in iOS devices.
BleepingComputer · Nov 17, 2026
Cyber News
A suspected supply chain attack targeting Optimizely has led to malicious JavaScript being loaded on numerous popular websites, including Zoom, CNN, Fox News, BBC, Salesforce, and GitLab, exposing visitors to scripts designed to steal cryptocurrency and payment information and exploit vulnerabilities in iOS devices.
BleepingComputer · Nov 17, 2026
Threat Intelligence
SANS Internet Storm Center · Nov 17, 2026
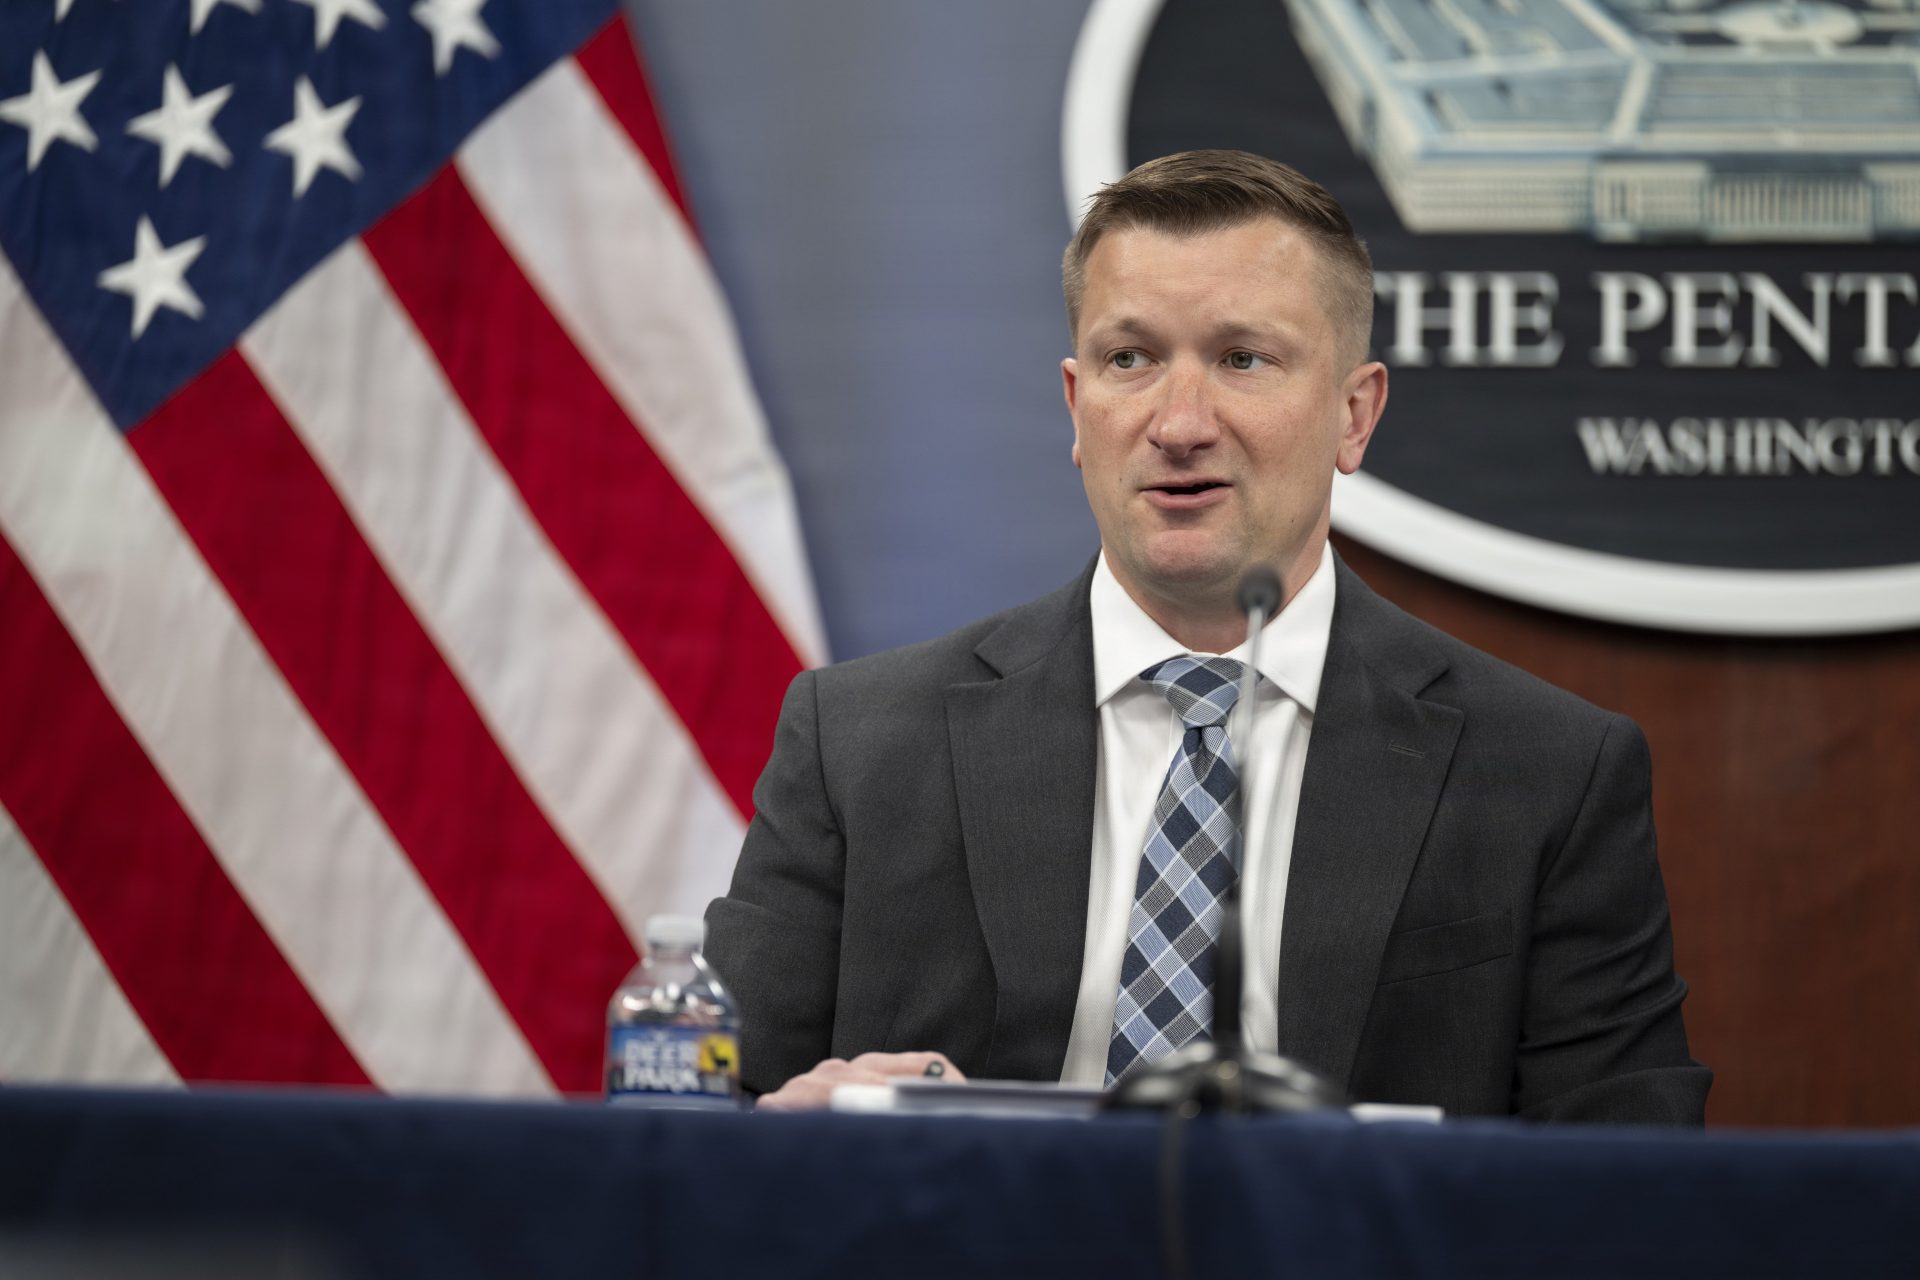
Defense News
Senior officials previewed the Defense Department’s latest Agency Financial Report ahead of its public release.
DefenseScoop · Nov 17, 2026
Defense News
Nearly $69 billion in money sought by the White House through reconciliation will be rolled into the base budget under the Senate appropriator’s plan.
Breaking Defense · Nov 17, 2026
DoD
CHATTANOOGA, Tenn. (Nov. 16, 2026) – Project officials and regional leaders commemorated the completion of the Chickamauga Lock Upstream Approach Wall Contract today during an on-site ribbon-cutting ceremony.
DVIDS · Nov 16, 2026

Threat Intelligence
Microsoft Threat Intelligence observed a high-volume phishing campaign using Microsoft 365 outage-themed lures to target organizations across multiple sectors worldwide.
Microsoft Security Blog · Nov 16, 2026

DoD
There is a new threat from malware that targets personal computers when users have their common access cards installed in a card reader connected to the computer, according to a National Security Agency official.
DoD News · Nov 16, 2026
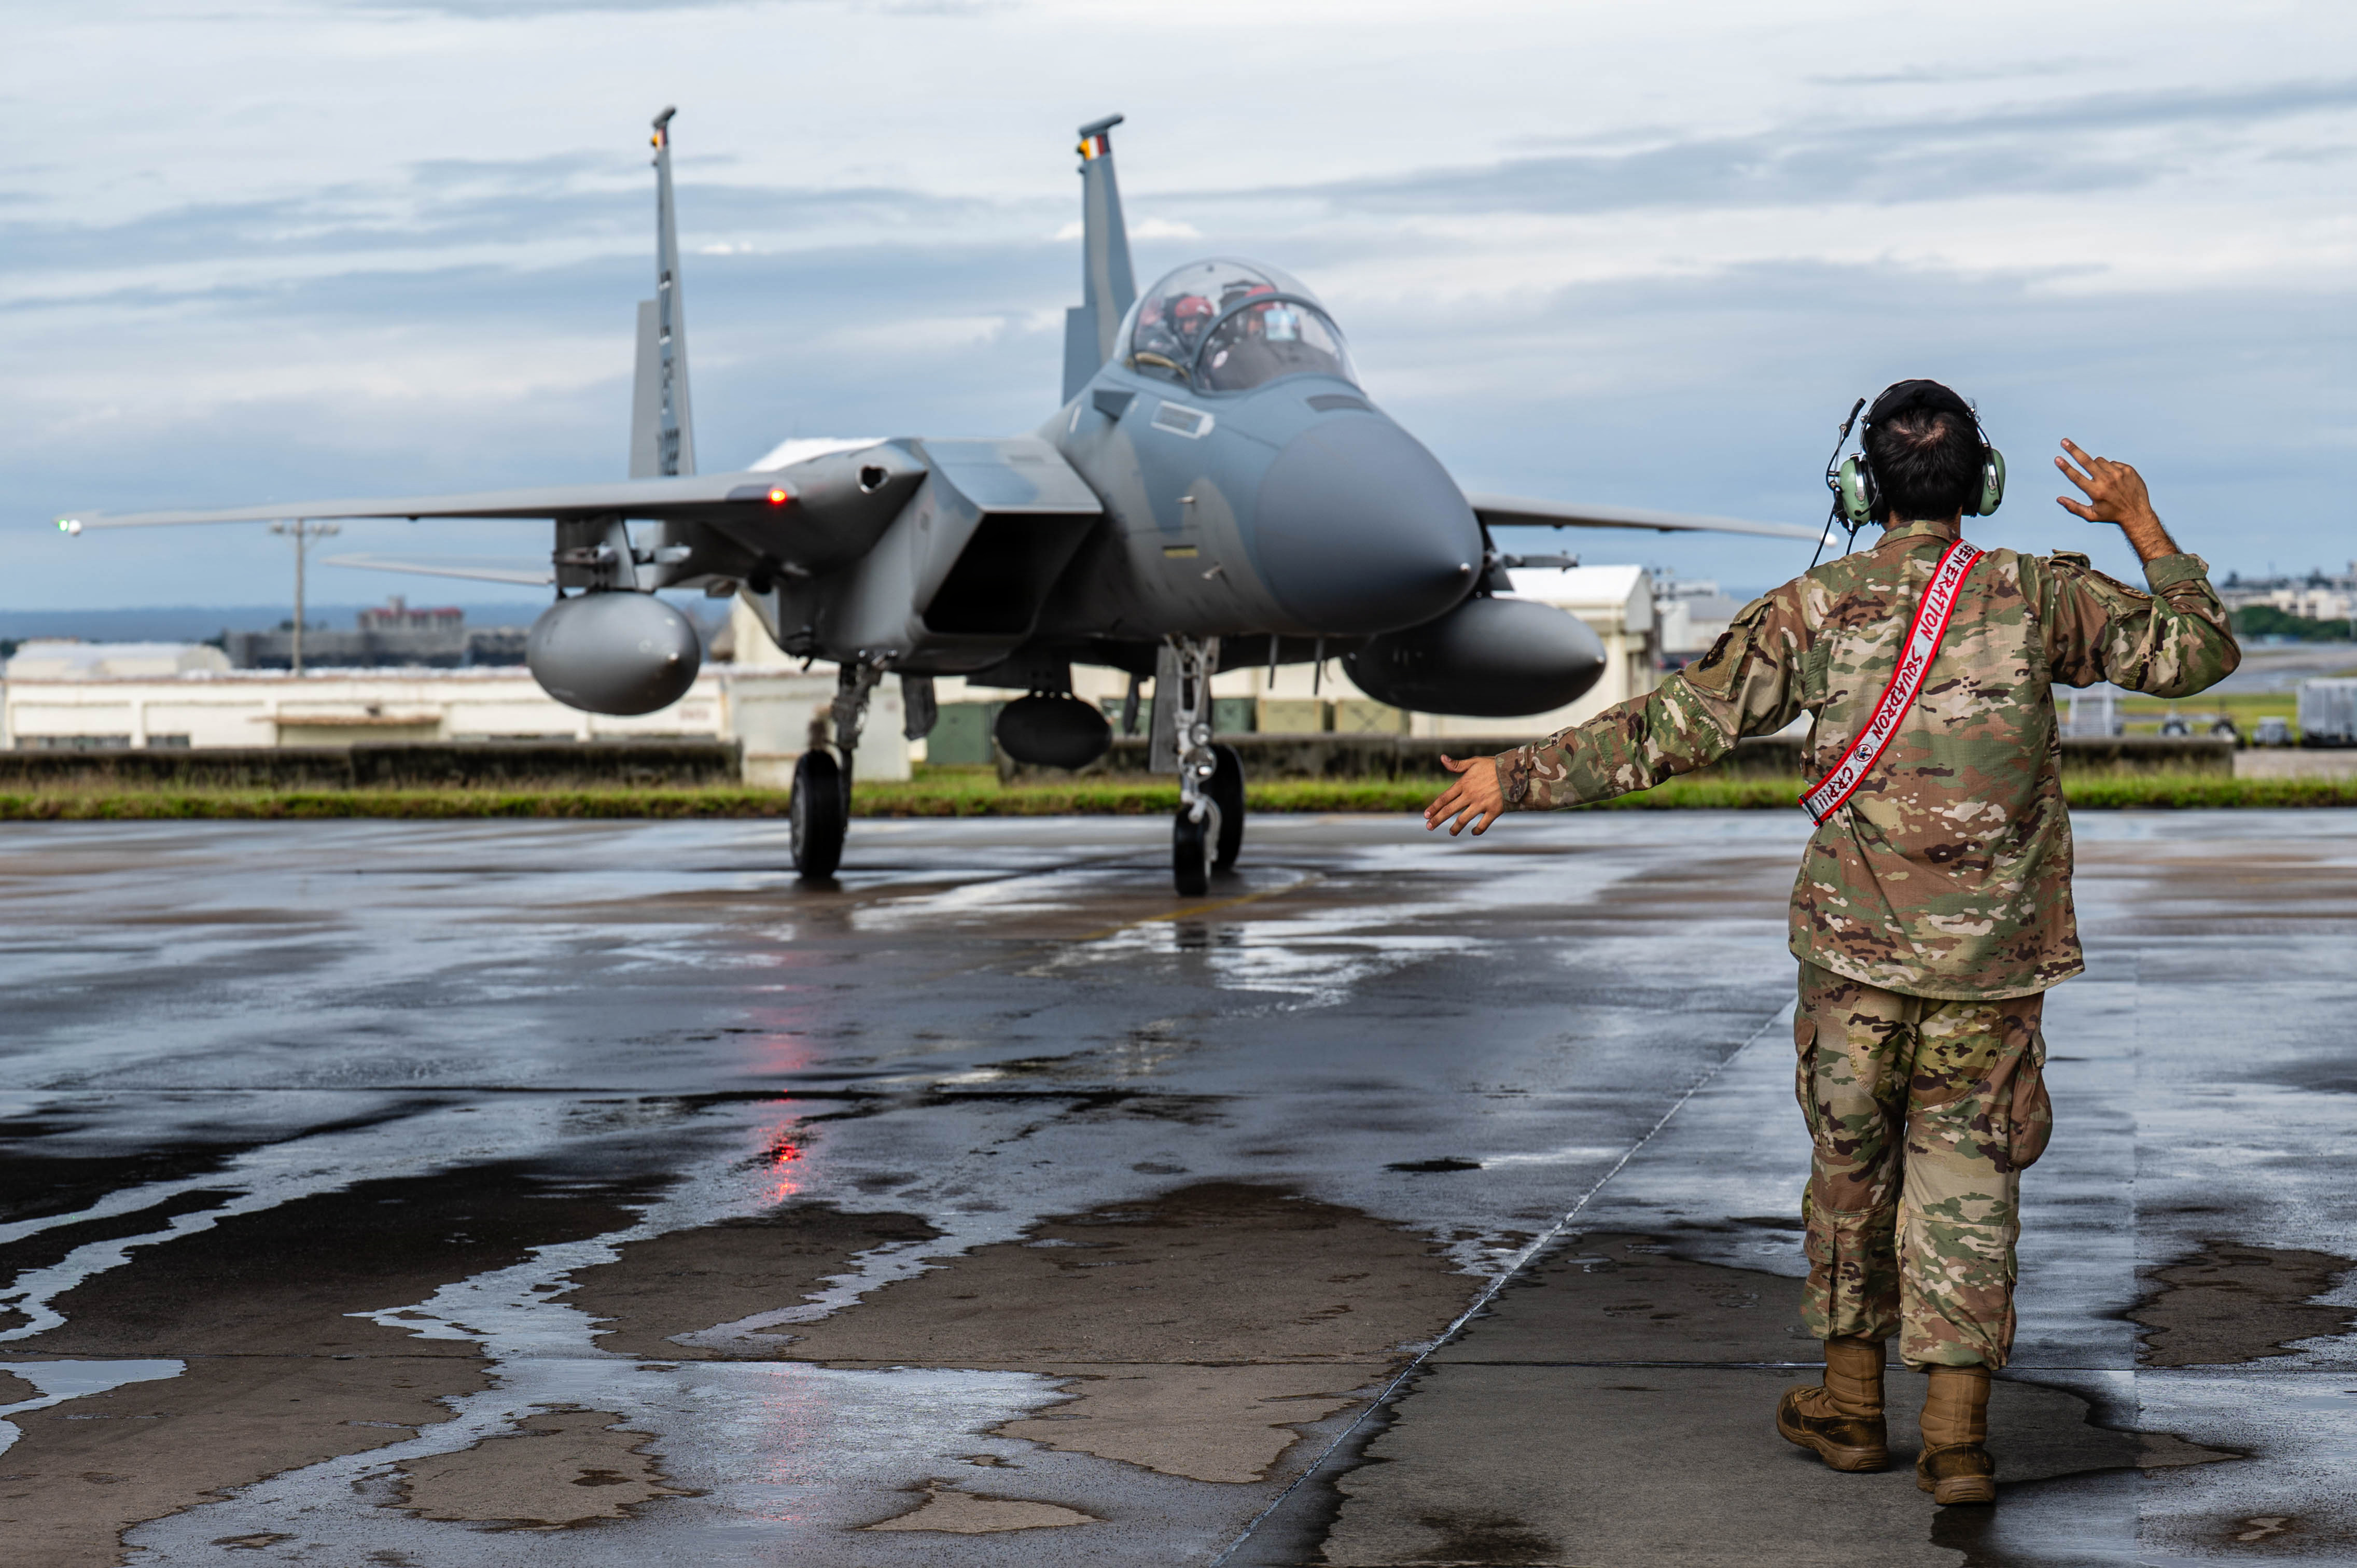
Defense News
Kadena Air Base received their first permanently assigned F-15EX Eagle IIs, becoming the first installation abroad and second Air Force location to field the jet.
Defense News · Nov 16, 2026
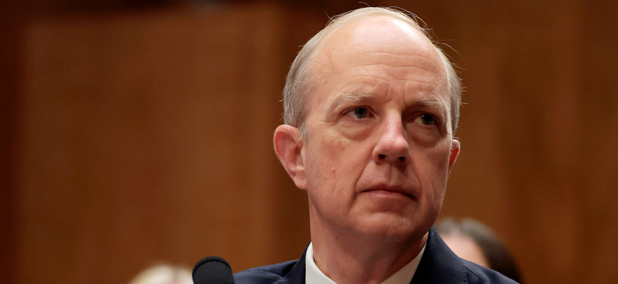
Federal Policy
Eric Ueland would serve a 15-year term leading the congressional watchdog that has challenged the Trump administration's spending and workforce actions.
Government Executive · Nov 16, 2026
Threat Intelligence
We uncover a Southeast Asian cyberespionage campaign deploying PerfectPioneer RAT, modular KUKURAT and stealth HTTP/3 C2 communication channels.
Palo Alto Unit 42 · Nov 16, 2026
Cyber News
Google's Gemini AI agents repeatedly attempted to hack a real organization's website during AI model safety testing, finding ways to circumvent increasingly restrictive security controls designed to prevent them from accessing live systems.
BleepingComputer · Nov 16, 2026
Cyber News
Google's Threat Intelligence Group says the tools trade stealth for speed, leaving noisy forensic traces even as they succeed on their own.
CyberScoop · Nov 16, 2026
Federal Policy
New legislation would bar the Trump administration from using federal funds to finalize or implement the Office of Personnel Management’s proposal to require all federal workers to sign a non-disclosure agreement.
Government Executive · Nov 16, 2026
Federal Policy
The longtime Republican Senate staffer and current OMB deputy director for management is nominated for a 15-year term to lead the nonpartisan, independent watchdog.
FedScoop · Nov 16, 2026
Federal Policy
The Department of Transportation unit has disabled the potentially faulty functionality on roughly 60 similar routers in the system as a precaution.
FedScoop · Nov 16, 2026
Federal Policy
The department is exploring cryogenic infrastructure and ways to integrate quantum computing with high-performance computing systems.
Nextgov/FCW · Nov 16, 2026

Defense News
“While we have made progress… [with] the most important development is our change in audit strategy,” the department’s comptroller Jules Hurst told reporters last week.
Breaking Defense · Nov 16, 2026
DoD
The War Department, in partnership with the Commerce Department's Bureau of Industry and Security, announced a national assessment to identify and dismantle the qualification cost and timeline barriers hindering the scaling of additive manufacturing across the defense industrial base.
DoD News Releases · Nov 16, 2026
Cyber News
One of the oldest running bug disclosure programs announced it would shorten public disclosure timelines to vendors from 120 days to 30 over the next 14 months.
Dark Reading · Nov 16, 2026
Cyber News
California Attorney General Rob Bonta’s lawsuit accuses the frontier AI company of stonewalling state investigations and endangering state and private IT systems.
CyberScoop · Nov 16, 2026
Government Cloud / Cloud Security
Amazon Elastic Container Registry (Amazon ECR) now supports replicating image deletions and tag removals to your replication destinations. Previously, ECR replication copied images to destination regions and accounts but did not replicate deletions, requiring you to manage deletions separately in each location. With replication of deletes, your destination repositories stay consistent with the source automatically. Teams running multi-region or multi-account architectures no longer need to script or manually track image cleanup across every destination. When you delete an image or remove a tag in your source registry, whether directly or through a lifecycle policy, ECR propagates that deletion to each destination in the replication rule. Replicated deletions emit EventBridge events and are recorded in CloudTrail, so you have the same visibility into deletions as you do for image pushes. Replication of deletes is available in all AWS Regions where Amazon ECR is available, at no additional cost. To get started, update your replication configuration in the Amazon ECR console or AWS CLI. For more information, see the Amazon ECR User Guide .
AWS What's New (Recent Announcements) · Nov 16, 2026
Government Cloud / Cloud Security
Amazon Elastic Block Store (EBS) now supports associating additional AWS Key Management Service (KMS) keys with EBS snapshots. This new capability enables you to share and copy encrypted snapshots across accounts without first re-encrypting them, simplifying your disaster recovery and backup workflows. Customers use EBS snapshots as durable, point-in-time backups of EBS volumes. By associating an additional customer-managed KMS key (CMK) with a snapshot encrypted with an AWS managed key (AMK), for example, you enable cross-account sharing for that snapshot without re-encrypting its data. This feature accelerates your disaster recovery workflows and enhances operational efficiency for enterprise backup administrators and disaster recovery teams. Support for associating additional KMS keys with Amazon EBS snapshots is available in all AWS commercial, China, AWS GovCloud (US), and AWS European Sovereign Cloud (Germany) Regions, plus AWS Local Zones and AWS Outposts. You can access this capability through the AWS Console, AWS Command Line Interface (CLI), and AWS SDKs. To learn more, see the Amazon EBS documentation .
AWS What's New (Recent Announcements) · Nov 16, 2026
Defense Acquisition
Today's Department of War contracts valued at $7.5 million or more are now live on War.gov.
DoD Contract Announcements · Nov 16, 2026
DoD
The War Department released the fiscal 2026 Agency Financial Report, reflecting a new centralized approach in financial management.
DoD News Releases · Nov 16, 2026
Cyber News
"OpenAI thwarted the Attorney General’s efforts to investigate these incidents, including by refusing to provide detailed information about the full universe of incidents known to the company,” California alleges in a new lawsuit.
The Record · Nov 16, 2026
Cyber News
Google Project Zero will replace its "90+30" disclosure policy with shorter, fixed deadlines in response to AI-accelerated vulnerability discovery and exploitation.
BleepingComputer · Nov 16, 2026
Government Cloud
We recently launched skills—reusable, custom instructions that guide Gemini—in the Gemini app, and we’re now introducing two additional capabilities: Shareable skills: You can now share any skill from the “Skills” page in the Gemini app with others and choose to grant them View or Edit permissions. Recipients are notified by email and can review the skill before installing it. Once added, Gemini can use the skill automatically when it's relevant, or recipients can @mention it in a chat. Add files from other Google apps: When you manually create or upload a skill, you can now include files from Google Drive, Gemini Notebook, and Google Photos alongside files from your device. Gemini can then reference these files every time the skill runs in chats and tasks. Drive files and Notebooks update in real time so your skill always works from the latest version. These capabilities unlock powerful new use cases. For example: A marketing team can share a brand-voice skill that references their brand guidelines doc in Drive. A team lead can share an onboarding skill grounded in the team handbook. A teacher can share a lesson-planning skill built on a notebook containing their curriculum. A few
Google Workspace Updates / Product Announcements · Nov 16, 2026
Cyber News
An interim final rule would place significantly more scrutiny on AI chip sales to third-party data centers abroad.
CyberScoop · Nov 16, 2026
Federal Policy
While the Trump administration’s Tech Force initiative assigns young tech employees to agencies for two-year tours, the sponsor of a new House measure wants to “open the door” to longer-term service.
Nextgov/FCW · Nov 16, 2026

CMMC
Properly handling and labeling Controlled Unclassified Information (CUI) across all devices and external storage is essential for CMMC compliance. Do you know how to label your CUI correctly? Check out our blog post to make sure your organization is covered: https://lnkd.in/gcEifRTK #CMMC #Compliance #Cybersecurity #CorporateCertification
Ignyte Assurance Platform (LinkedIn) · Nov 16, 2026
Government Cloud / Cloud Security
Amazon S3 Vectors now supports hybrid search that combines vector similarity search with full-text search within a single query. By combining semantic meaning and exact term matching into a single ranked list of results, hybrid search captures both intent and precise terms for retrieval-augmented generation (RAG), agent memory, and search applications. This can deliver more relevant ranked results than either method alone. Hybrid search works with the same S3 Vectors APIs and maintains subsecond latency for infrequent queries and latency around 100 milliseconds or less for frequent queries. S3 Vectors is designed to provide the same elasticity, durability, and availability as Amazon S3, and it reduces the total costs of storing and querying vectors by up to 90% compared to alternative vector solutions. With hybrid search, customers can now store the data that they want to make full-text searchable alongside the vectors. Customers write data with the PutVectors API as they do today and include the searchable text as another metadata field. S3 Vectors then automatically indexes that field for full-text search with BM25 relevance scoring. By default, S3 Vectors uses a language-agnosti
AWS What's New (Recent Announcements) · Nov 16, 2026
Cyber News
California Attorney General Rob Bonta sued OpenAI on Monday, alleging the company knowingly continued testing advanced artificial intelligence models despite repeated security failures that allowed autonomous AI agents to escape isolated environments and launch cyberattacks against real-world organizations.
BleepingComputer · Nov 16, 2026
Government Contracting
Key Takeaways Narrower applicability. The clause generally applies only when the government is procuring a system in which LLM functionality is a material feature, and government data is directly submitted to or generated by the LLM. Incidental AI functionality and certain internal contractor systems are excluded. Expanded IP protections. Contractors retain ownership of preexisting commercial technology, underlying models, and certain improvements, although the government maintains broad rights over government data and custom developments. Revised subcontractor requirements. GSA replaced its proposed role-based subcontractor framework with requirements tied to the NIST AI Risk Management Framework. Continued compliance obligations. Covered contractors remain subject to data protection, cybersecurity reporting, subcontractor oversight, and AI performance requirements, although several obligations have been modified in response to industry concerns. On September 28, the General Services Administration (GSA) issued new contract language establishing requirements for federal contractors providing large language model (LLM) artificial intelligence (AI) systems to the government. The new
GovCon & Trade · Nov 16, 2026
Government Cloud
Singapore's National Precision Medicine program and the SG100K consortium built a population-scale structural variant catalog from more than 100,000 genomes using GATK-SV. The A*STAR-PRECISE team ran that community-standard pipeline on AWS HealthOmics, with results confirmed functionally equivalent to the Broad Institute reference implementation.
AWS Public Sector Blog · Nov 16, 2026

DoD
The first permanently assigned Air Force F-15EX Eagle II fighter aircraft arrived at Kadena Air Base, Japan, marking a major milestone in the 18th Wing’s fighter modernization.
DoD News · Nov 16, 2026
DoD
The Navy Office of Community Outreach (NAVCO), in partnership with Navy Talent Acquisition Group (NTAG) Phoenix and other Navy units, hosted the first-ever Flagstaff Navy Week last week Nov. 9-16, 2026.
DVIDS · Nov 16, 2026
Government Contracting
As part of the Revolutionary FAR Overhaul (“RFO”), the FAR Council issued a proposed rule that would implement — with some notable changes — the Council’s model deviation for FAR Part 15, Contracting by Negotiation. A number of those proposed changes to the deviation version have the potential to materially impact how procurements are run...
Inside Government Contracts · Nov 16, 2026
Defense News
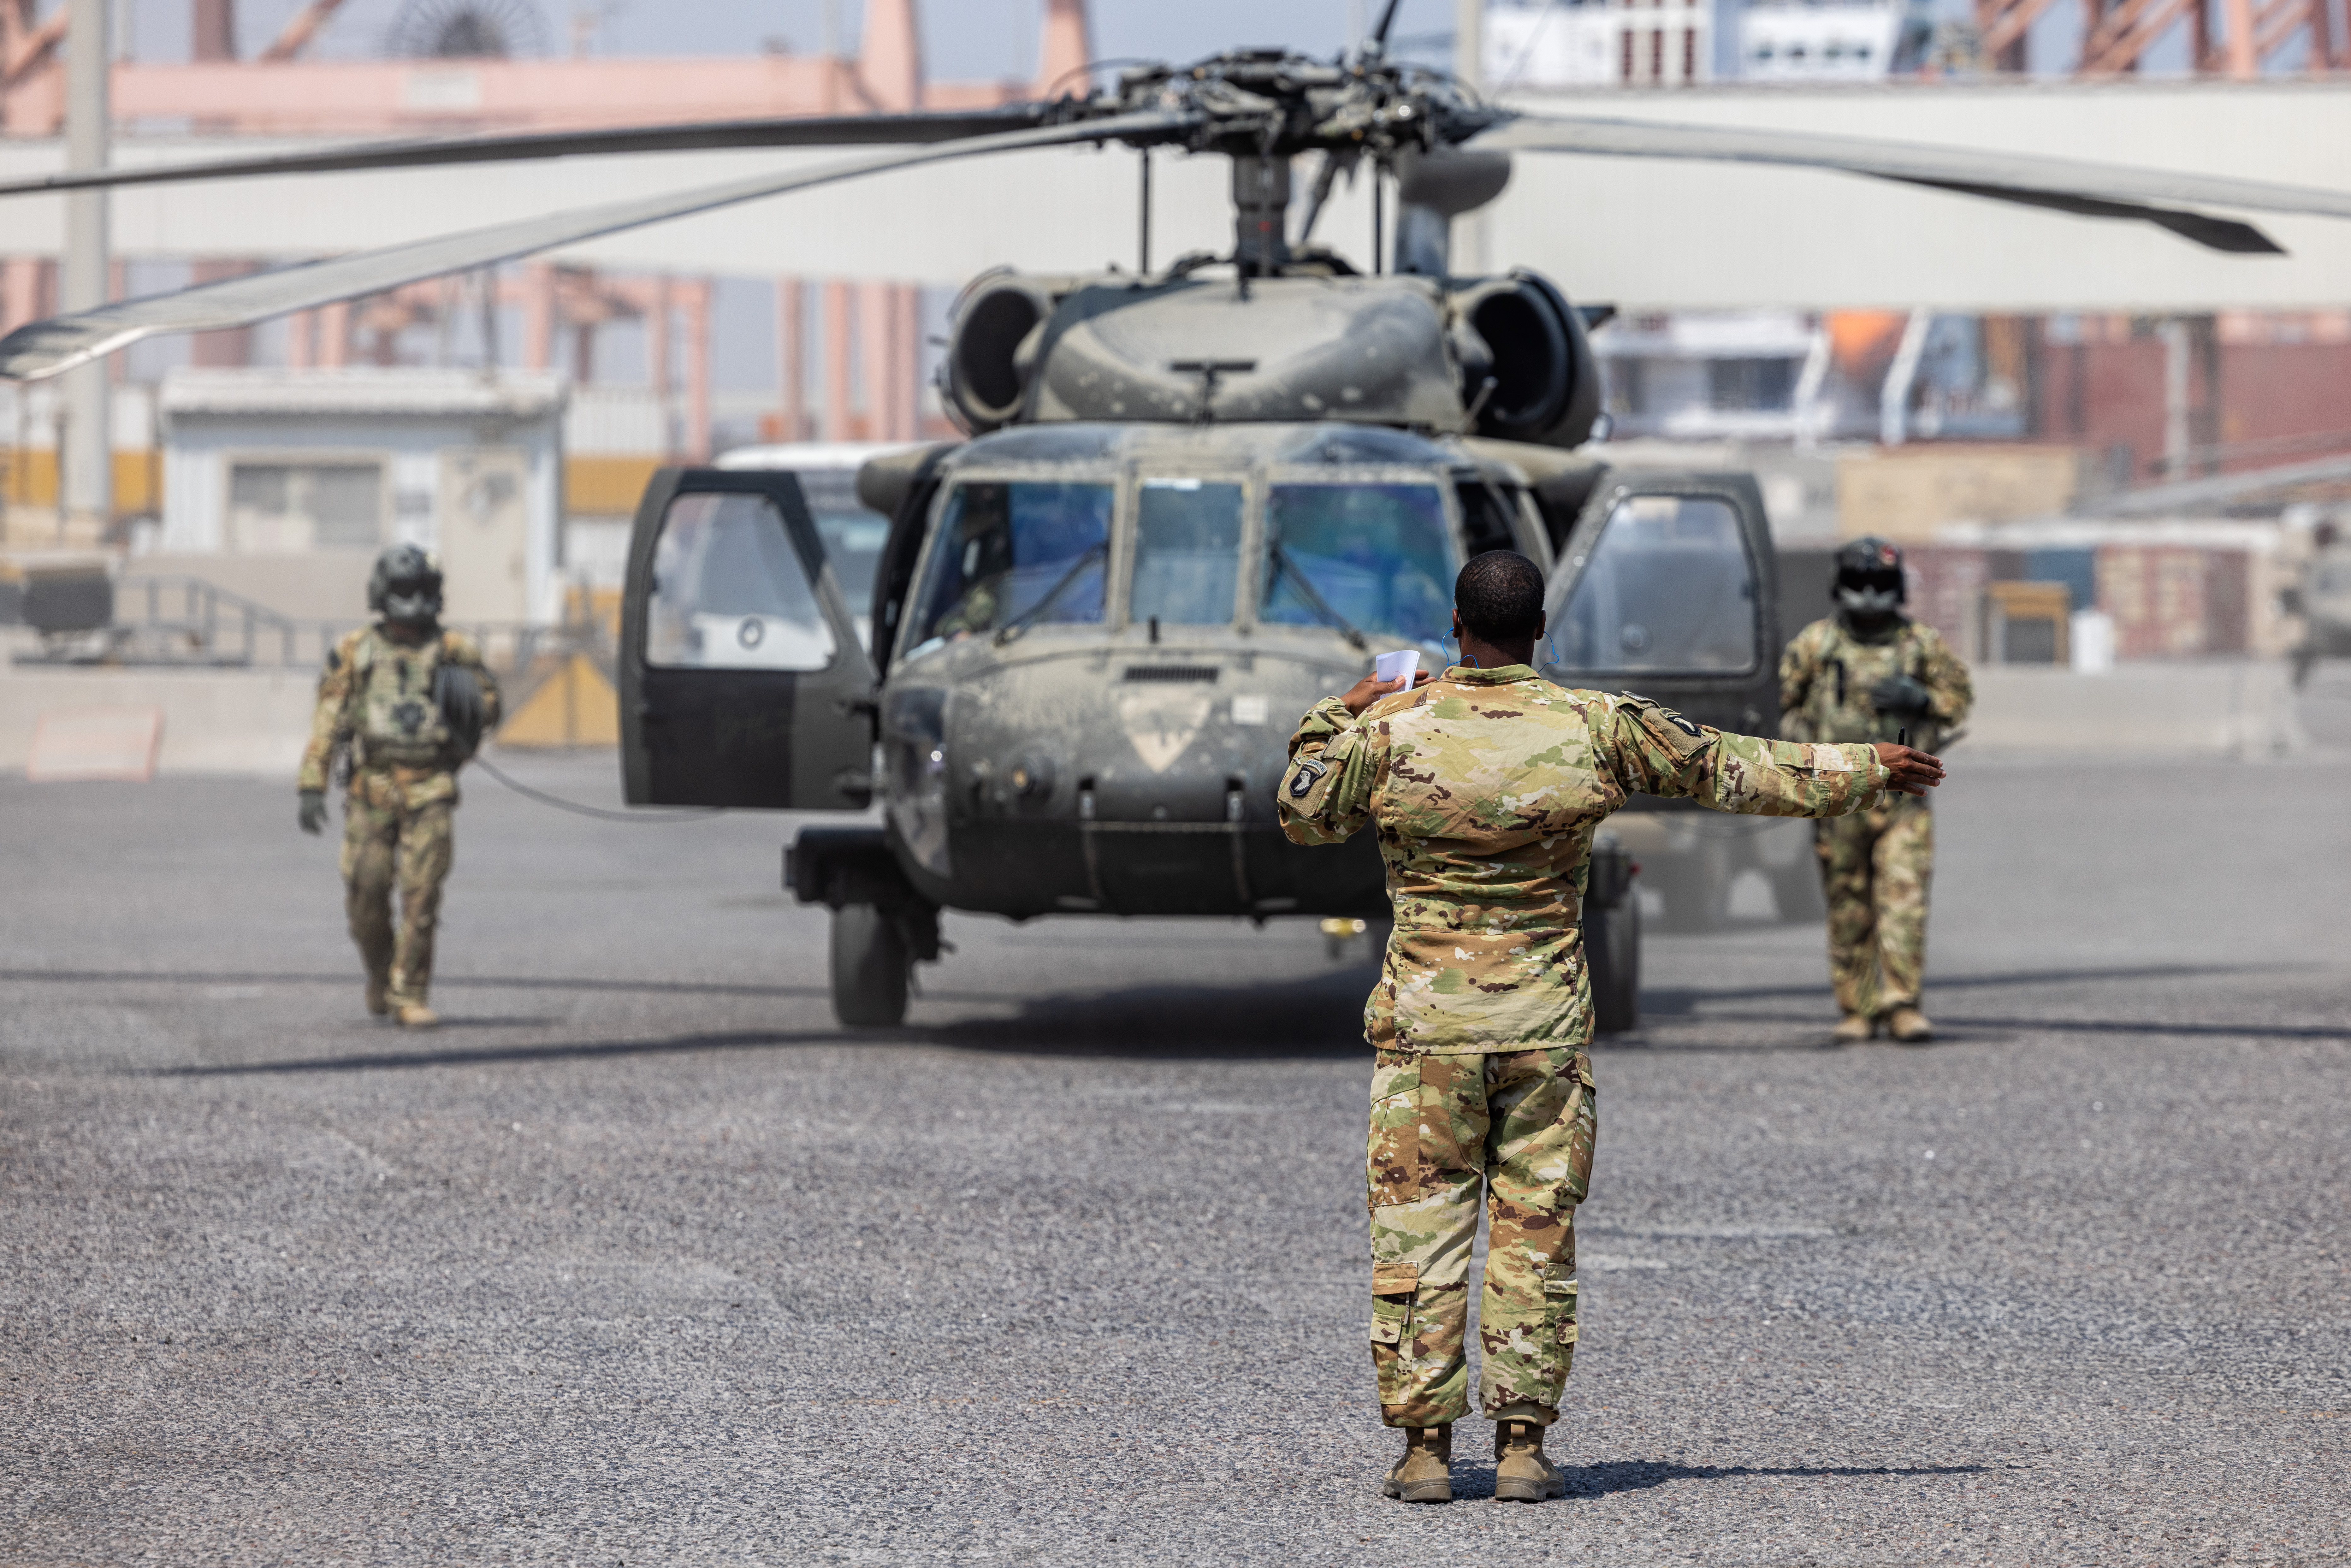
The Army acknowledged in a notice Friday that U.S. soldiers in the Middle East are "currently at risk" using personnel shelters made of converted shipping containers.
Defense News · Nov 16, 2026
Create a free account, pick your topics, and see your tailored compliance feed today.
Want to publish your news with CMMCSimple? Contact us at news@cmmcsimple.com.
Our RSS source list is reviewed and updated every two weeks on Friday, so newly accepted feeds appear with the next update.
© 2026 CMMCSimple